GDPR compliant AI — Can it block a forbidden action?
A badge cannot enforce privacy. Trace every data hop, narrow agent authority, and block external actions…
The short version
- GDPR compliant AI requires controls across every data flow, vendor, user-rights process and external action.
- A Finality Sink can hold agent actions until purpose, recipient, jurisdiction and revocation checks pass.
- Teams must test deletion, narrow permissions and block unauthorised consequences before real personal data enters production.
A €300,000 fine is an expensive way to learn that deleting someone’s data is only half the job. In its July 2026 EXTIA decision, France’s CNIL found candidate records were sometimes deleted automatically while erasure requesters waited for an answer.
More than three-quarters of the previous year’s 265 requests were mishandled or handled unsatisfactorily. Automatic deletion did not remove EXTIA’s duty to report the outcome. Silence from a database was never going to count as customer service.
That distinction is the whole meal, not the parsley.
I flinch when a vendor promises GDPR compliant AI on a sales slide. I once stared embarrassingly long at a green “EU GDPR Ready” badge before asking whether deleted conversations also vanished from debugging logs. The answer took three people, two follow-up emails and no verb meaning “delete.”
Compliance covers the entire operation: why data enters, who accesses it, where it travels and what happens after the model responds. An AI agent with broad database credentials can cross those boundaries in milliseconds while your privacy policy loads in another tab.
Follow one prompt until it disappears
A model cannot wear GDPR compliance like an organic sticker on Parmigiano. One deployment might forecast equipment failures from anonymous sensor readings; another retrieves Elena Rossi’s invoices, address and complaint history. Different data paths and consequences create different obligations.
Here is the mechanism I map before approval. A person submits a prompt through an application that may save the raw message. A retrieval service searches a vector store and adds records. The combined context goes to a model provider, while an observability service may receive traces containing the same information. The response returns and may enter a CRM, ticketing system or agent memory. Every hop adds a recipient, retention decision and location where access or erasure requests may need to propagate. Compliance follows the chain from collection through deletion, including the agent’s final action.
Purpose limits must survive that journey. Permission to read an address for delivery support does not cover training a general model on the conversation. If a supplier uses prompts for its own objectives, the GDPR role analysis may change because it has chosen its own purpose.
I classify workflows separately under the GDPR and AI Act. Personal-data processing triggers the first analysis; intended use drives the second. A recruitment tool may fall under both, while a machine-failure model using non-personal readings may have no GDPR issue. Controller and processor roles also differ from AI Act categories such as provider and deployer. European law has many maps. Naturally, each uses a different legend.
The model itself needs scrutiny when training involved personal data. The EDPB’s Opinion on AI models says anonymity must be assessed case by case, including whether information about a person can be extracted. I would not assume every model is a searchable filing cabinet, but “the weights are anonymous” is not a magical incantation.
Before launch, I want the exact purpose, minimum necessary data, every recipient and every storage location in writing. Then show me the lawful basis and working routes for access, correction, objection or erasure wherever applicable. “Our trusted ecosystem” is procurement poetry. A data-flow map names systems and deletion paths.
The trust page is where optimism goes to hide
I read the architecture diagram before the trust page. A DPA can allocate processor duties, and EU hosting can restrict storage geography. Neither tells me whether one overpowered agent tool lets an employee retrieve the whole customer database.
A proper vendor review follows one request end to end. I check where the application logs it, which service retrieves data and whether support staff can inspect the resulting prompt. I trace the output downstream and test deletion across every copy. Each contractual promise must connect to a demonstrable setting, scheduled job or access rule. If limited retention is promised while debugging keeps prompts indefinitely, the prettier document loses. A signature proves DocuSign worked that afternoon; technical behaviour proves the arrangement works.
Tirza AI’s published DPA shows why details matter. It requires breach notification within 48 hours, alongside the broader requirement to notify without undue delay. Retention varies by format: call transcripts can remain for two years, while audio lasts 30 or 90 days. A caller may persist across several systems after one file disappears. The supplied material does not establish whether Tirza’s deletion commitments are independently audited across its sub-processors. I would ask for evidence, not fill the gap with positive vibes.
EU hosting deserves equal scepticism. Ifri argues localisation cannot deliver sovereignty while dominant providers remain subject to non-European laws such as the US CLOUD Act and FISA. A Frankfurt region controls geography; corporate ownership and legal reach are separate layers.
Complete technological independence sounds lovely until someone buys the servers. In a September 2026 survey of 1,300 business and technology executives, 59% said full digital sovereignty was unrealistic and favoured managed dependence around critical operations. Karine Brunet put it plainly in the Capgemini Research Institute release:
Today’s organisations operate in highly interconnected technology ecosystems where complete independence is rarely achievable.
I agree, and it strengthens Europe’s case. Combined European providers hold about 13% of Europe’s cloud market, while three US hyperscalers control most of it, according to Open Future’s 2026 policy brief. Europe needs shared procurement, interoperable sovereign-cloud standards and EU-level investment large enough to create credible alternatives for sensitive workloads. Twenty-seven national vanity clouds would recreate the Holy Roman Empire with Kubernetes.
Former European Commissioner Thierry Breton captured the political problem with brutal efficiency in his interview with DSIN de l’année:
La confiance s’est effondrée.
Europe rebuilds trust by owning more of the stack and strictly limiting infrastructure it does not own. Federal coordination gives European providers a continental market; fragmented national schemes give consultants more PDFs.
Put the brake at the point of action
An AI workload can access several data sources and trigger an external action before consent checks or auditors intervene. Once an email is sent, datasets are joined or a tool changes a record, governance becomes cleanup.
A recent Internet-Draft proposes separating an agent’s reasoning from the moment its action takes external effect. After authentication and model reasoning, the system expresses a proposed disclosure, transfer or tool invocation as a “Candidate Act.” It remains non-effective while a protected process checks the minimum required data, identity, approved purpose, recipient, destination, jurisdiction, applicable policy and current revocation state. Failure freezes the action. Success creates authority cryptographically bound to that exact operation. At the external boundary, a “Finality Sink” verifies the required state before any email, API call or database write occurs. Change a load-bearing parameter, such as the recipient, and the system must evaluate a new Candidate Act.
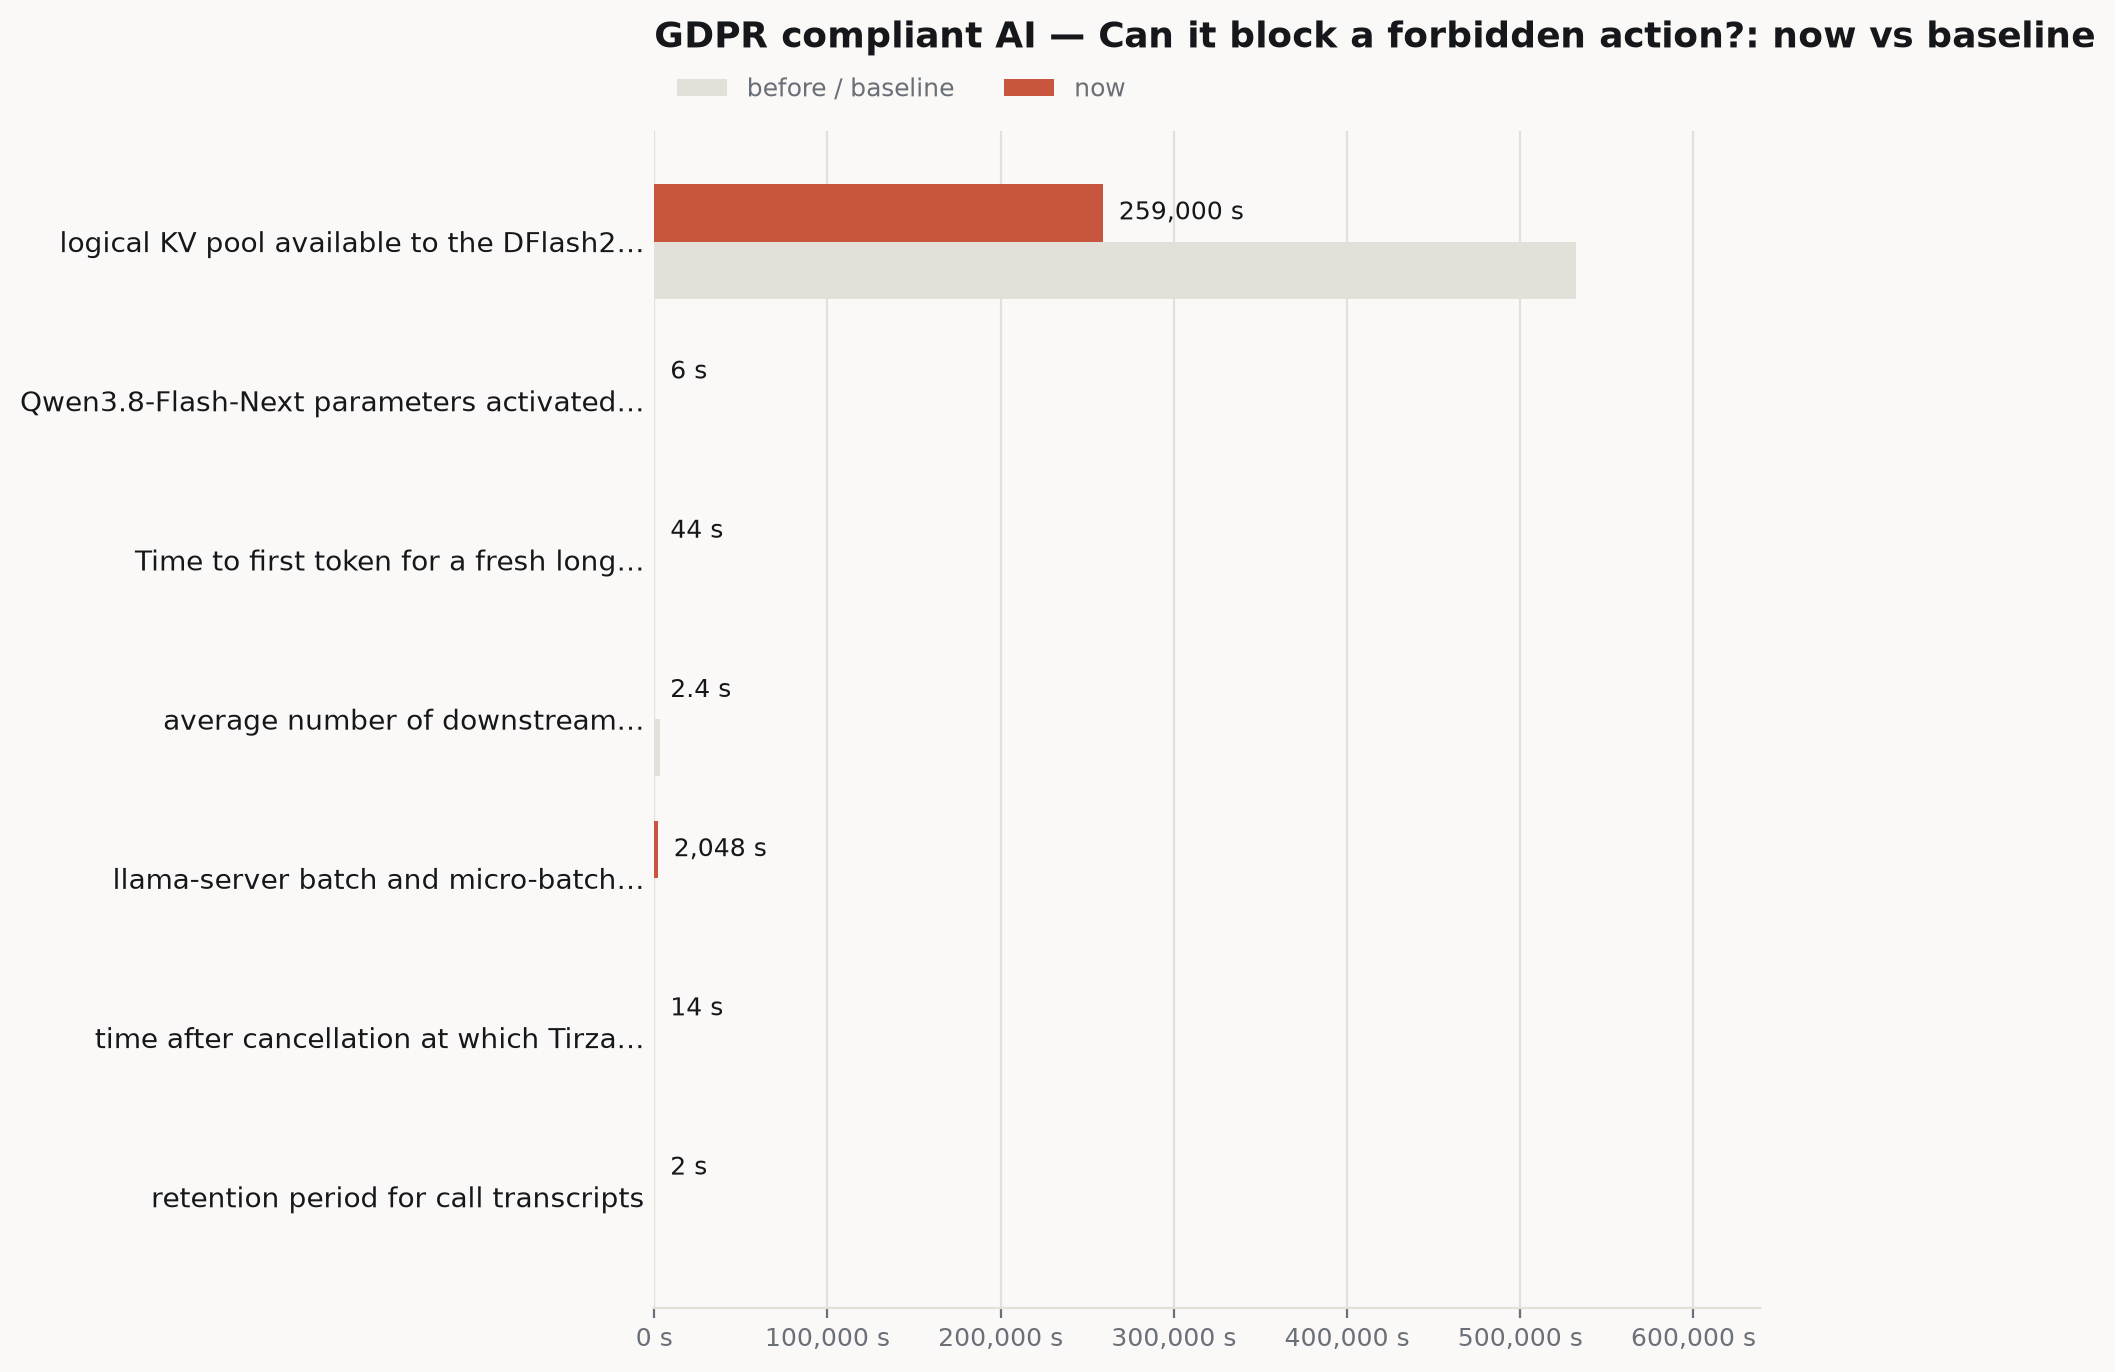
That beats asking the model whether its own action seems authorised. Research on authority-spoofing attacks found configurations where models recognised forged authority but still produced the conflicting tool call. Average execution across the wider fleet was about 1%, yet deployment fingerprints within one window varied by as much as 47 percentage points from the least vulnerable configuration. A security boundary that changes with endpoint configuration is tiramisù left in a hot car.
The Loire hospital breach shows how broad authority expands the blast radius. In its September 2026 decision, the CNIL said one compromised account accessed records for about 525,000 patients because permissions were not limited to professionals involved in each patient’s care. The credentials exposed far more data than their owner needed, turning one account failure into hospital-wide exposure.
Weak authentication and delayed detection worsened the damage. The CNIL imposed a €500,000 penalty for inadequate security measures. An agent using those permissions would inherit the access and add machine speed—precisely why the final enforcement point matters.
The Candidate Act design remains a proposal. The supplied sources show no production deployment proving it prevents GDPR violations, nor measurements for latency, operational cost or false denials. I still want European teams testing it because enforcement occurs before the controlled consequence becomes irreversible.
A beta label changes nothing
A pilot using real personal data is already processing it. Five friendly customers and a “beta” label do not create a GDPR theme park where the rules wait outside.
My pre-launch process starts with a narrow ship record for each use case. It names an owner, permitted purpose and genuinely necessary data. Engineering converts those limits into retrieval scopes, retention jobs, tool permissions and approval gates. A rights test follows one fictional person through prompts, logs, vendors and downstream applications. A boundary test asks an authorised user to retrieve or send information beyond the approved purpose. The team rehearses disabling access after a simulated incident and identifying affected people. Any failure keeps real customer data out until fixed.
A DPIA belongs early whenever high risk is likely. Recruitment systems are obvious examples because profiling and employment decisions can substantially affect people, and the AI Act treats many employment uses as high-risk. Starting the assessment the night before launch is like learning at dinner that the ragù needs four more hours. Technically, cooking has begun.
Rights handling needs equal engineering attention. In the EXTIA case, 166 requesters received no outcome and another 27 were answered late. The database may have completed part of the deletion; the organisation still failed the person outside it.
Europe can turn regulatory pressure into product advantage. I want EU-funded reference implementations for pre-effect enforcement, shared testing across member states and procurement that gives European agent-security companies a continental home market. Federal coordination builds AI champions able to compete with American and Chinese platforms while preserving European control over sensitive infrastructure.
By 2028, serious European agent platforms will sell purpose-bound execution by default, holding external actions at a Finality Sink until their authority checks out. Whoever builds that layer will offer something worth far more than a green GDPR badge: customers can watch the system refuse to cross the line.
Frequently asked questions
What makes AI GDPR compliant?
AI is GDPR compliant when its entire operation has a lawful purpose, uses only necessary data, limits access and retention, supports applicable user rights, and controls every recipient and external action. Compliance follows personal data from collection through retrieval, model processing, logs, downstream systems and deletion.
Does EU hosting make AI GDPR compliant?
EU hosting restricts storage geography but does not by itself establish GDPR compliance. Corporate ownership, foreign legal reach, overbroad permissions, processor practices, debugging logs, subprocessors and downstream copies remain separate concerns. A Frankfurt region cannot replace purpose limits, deletion testing, access controls or a complete data-flow map.
How can AI agents be stopped from taking unauthorised actions?
AI agents can be stopped by separating model reasoning from external effect. The system holds each proposed disclosure, transfer, email, API call or database write as a Candidate Act until a protected process verifies purpose, identity, recipient, jurisdiction, minimum data and revocation state at a Finality Sink.
Sources
- Governing neuro-AI
- Agentic AI: what are we talking about?
- Artificial Intelligence and the Law. The Personal Data Protection Office invites you to the third Open Expert Lecture
- European Commission sends first requests for information to more than 30 AI providers
- EU governments revise GDPR pseudonymized data rules in new digital package compromise
- The European Union Artificial Intelligence (EU AI) Act, the General Data Protection Regulation (GDPR) and data protection rights: what UK organisations need to know