A critical PHP flaw stalled because its fixes created compatibility problems
PHP’s emergency releases fix two critical RCE flaws after AI-assisted research, scarce security resources and…
The short version
- PHP operators must immediately install patched releases because two critical flaws enable unauthenticated remote code execution.
- Supported branches require PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, followed by workload restarts and interpreter verification.
- AI-assisted research shortened exploitation work, while scarce runtime expertise and a broken embargo compressed defenders’ time.
Stop reading and patch PHP. PHP2Shell turned a memory bug spotted in 2024 into unauthenticated remote code execution; a broken embargo shortened defenders’ runway.
Move immediately to PHP 8.5.12 or 8.4.27. They replace vulnerable builds on PHP’s two newest supported branches.
Older supported branches need PHP 8.3.36 or 8.2.35, replacing the previous vulnerable maintenance releases. Vendor-maintained distributions may ship verified backports under different version strings. Restart Apache, PHP-FPM workers, containers or the whole workload, then verify which interpreter is running.
And yes, PHP itself. Updating WordPress, Drupal, Joomla, Laravel or that plugin installed during the Obama administration will not fix the runtime. Molto importante.
Brutally difficult vulnerabilities once bought defenders time. PHP2Shell killed that assumption. Frontier AI models are making exploits cheaper while projects like PHP fund runtime security like an ambitious weekend hobby. That should terrify anyone whose revenue sits behind a web server.
The runtime broke beneath the application
CVE-2026-109618 is the out-of-memory flaw. A request hits PHP’s memory limit while internal request data remains partly initialized. An allocation triggers a fatal bailout before setup finishes, but PHP’s bookkeeping says the unfinished entry exists. Cleanup later trusts that structure as valid. The resulting memory corruption can hand control to an attacker. PHP says researchers demonstrated full remote code execution under default Apache mod_php settings before application code ran. Your framework cannot save you; the engine has already lost control.
Imagine a restaurant ticket reaching the kitchen half-written, then the cooks preparing whatever garbage fills the blanks. Less funny when the kitchen runs your checkout page.
CVE-2026-109619 crosses between requests. A fatal error leaves request-owned state pointing to memory PHP frees when the request ends. The web server keeps the worker alive, preserving that dangling reference. A later request reaches it before normal initialization clears it, so PHP consumes freed memory as though the first request still owned it. The Foundation says code execution was demonstrated against a real application using mod_php, while application-level paths were confirmed on PHP-FPM. Both flaws affect memory management and error handling used by nearly every request. Ugly blast radius.
The official notice covers web installations using mod_php, PHP-FPM, php-cgi, FrankenPHP and LiteSpeed. Apache mod_php has the strongest documented pre-application route, but FPM fleets still need immediate patches.
Check your distribution’s advisory before trusting `php -v`. Ubuntu packages, for example, can backport fixes while retaining version strings below upstream releases. PHP also published minimal source backports for some older branches, though moving to a supported branch is saner.
Temporary configuration changes can block known paths. PHP lists removing the memory limit, restricting requests, disabling session upload progress and changing fatal-error backtraces on the newest branch. Web application firewalls can catch known payloads. None fixes the bug. Only a patched interpreter repairs PHP’s broken cleanup and stale-state behavior.
AI made an old flaw practical
A contracted PHP core developer first saw signs of the out-of-memory problem in 2024 while remediating a finding from Quarkslab’s external audit. The team suspected exploitation but lacked a concrete path to code execution, and every proposed fix created compatibility problems. Work repeatedly stalled because PHP has few people with deep engine expertise. Calif reported unconditional remote code execution with the same root cause on August 11, 2026, through the Patch the Planet program. OpenAI independently reported that root cause, while OpenAI and Wiz supplied more vectors. PHP says the evidence moved the flaw atop its security queue. The emergency response produced four maintenance updates, one replacing the vulnerable release on each supported branch.
AI-assisted vulnerability research changes the economics. A researcher can start with a suspicious crash or broken invariant, then use a model to trace attacker-controlled input through the engine, build a harness, test requests and inspect each failure. Another request can target a different PHP version or memory layout without manually rewriting every variation. Skilled humans still form the useful hypotheses, and no model can own a patch that breaks half the internet. But models grind through variations fast enough to make ugly memory-corruption chains practical. Difficulty buys less time now.
Those tools also cheapened security reports, and PHP’s inbox paid the price. From July through its report-handling post, PHP published 15 CVEs and closed 106 submissions that were duplicates, invalid claims, queued reports or failures to reproduce. PHP says manual handling had become unrealistic, so it increased automation and used AI to validate impact and group reports by root cause. A person still sets severity and writes or reviews every patch. Reporters hear back only after somebody attempts reproduction.
That split makes sense. Models excel at repetitive tracing. Institutional responsibility belongs to people who can explain why a clean-looking repair might break an extension last updated when everyone owned an iPod.
Julia Schottenstein described the partnership’s goal:
We're proud to bring that model into mission-critical enterprise operations through our partnership with DXC.
PHP’s patch process ran out of road
Known weaknesses can stall for rational reasons until the outcome becomes absurd. One maintainer changes fatal-bailout behavior; somebody finds an extension depending on the old lifecycle. A narrow fix preserves compatibility but leaves related state exposed. A broad one closes the pattern but may create a denial-of-service path or force changes on third-party maintainers. PHP’s security group required consensus, so unresolved trade-offs blocked a decision while scarce engine specialists returned to vulnerabilities with proven impact. Calif’s working exploit changed the math. The Foundation then funded several people full time, including weekends.
The PHP Foundation described the failure with unusual honesty:
We won't pretend otherwise: the delay was a structural failure, caused by both the security team's decision process and its lack of resources.
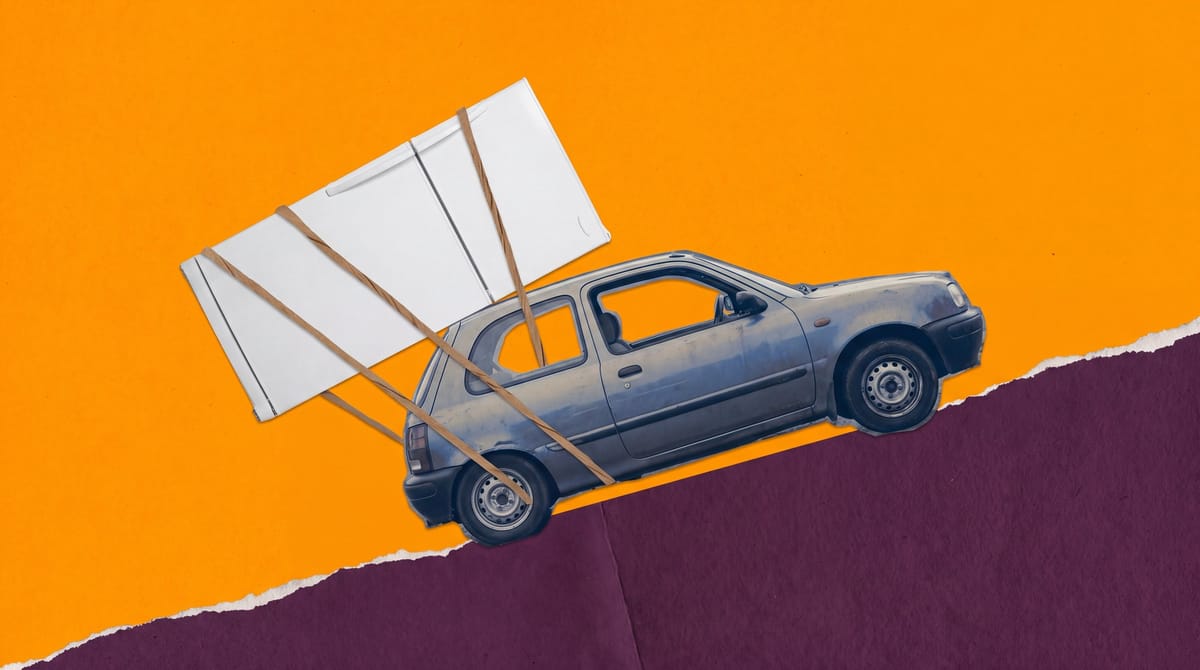
I respect the admission without mistaking it for absolution. A critical weakness waited too long. Still, shouting “fix it faster” at a tiny engine team is like asking a Fiat Panda hauling a refrigerator uphill to find sixth gear.
Generic headcount cannot replace runtime expertise. PHP needed people who understood memory management, extension compatibility and how each SAPI tears down requests. Ten random developers would mostly give the same specialists ten more reviews.
The Foundation had begun professionalizing security. It formed an Ecosystem Security Team in May, added Alexandre Daubois for triage and fixes in July, then brought Daniel Scherzer into hardening in September. Decisions are also shifting from strict consensus to majority votes with room for compromise. Helpful changes, though a few hires barely register against PHP’s footprint.
When cash got tight, I treated upstream funding as optional. I was wrong. Companies approve observability dashboards with seventeen gradients, then label runtime security sponsorship generosity.
If your business earns money on PHP, maintainer funding belongs in the infrastructure budget. Charity is buying raffle tickets at the neighborhood festa. Paying people who protect production revenue is supplier management.
The embargo joined the incident
Coordinated disclosure leaked before defenders were ready. CVE identifiers and an incorrect perfect severity score circulated publicly, though the first leak reportedly lacked technical exploit details. It still showed attackers where to dig, so PHP advanced the announcement. Maintainers needed distributions to finish packages and hosts to prepare deployments. Immediate source publication would expose the patch diff while many operators had nothing installable. PHP accelerated the schedule by one day, preserving some preparation time as secrecy collapsed. Calif then mistakenly published a proof-of-concept video. Deleted copies spread, because the internet has never respected a delete button.
Cloud providers were already moving. Cloudflare says it deployed managed WAF protections about nine hours before public disclosure rather than waiting, then watched attackers mutate payloads around its rules. Its detection examined requests and origin responses because multipart traffic alone could not reliably distinguish exploitation from legitimate activity. Cloudflare still told customers to patch. A firewall cannot inspect PHP worker memory or cover every server-side path.
Amazon’s telemetry makes the timeline weirder. MadPot observed an apparent exploitation attempt on October 17, four days before the October 21 disclosure. Amazon says it cannot determine how the actor obtained exploit information or whether the attempt would have worked against a real deployment.
The dates beg us to blame the leak: exploit information escaped, then someone tried exploiting the flaw before disclosure. But Amazon’s earliest observation predates the public proof-of-concept leak, and its telemetry cannot prove the actor had a working chain. The embargo breach may be connected. The current evidence does not get us there.
I would hunt from at least that earlier date for suspicious multipart POST requests containing `PHP_SESSION_UPLOAD_PROGRESS`, followed by unexpected child processes or file changes on PHP hosts. Review crashes and unusual worker restarts too, though clean logs prove little.
Nobody knows whether any pre-disclosure attempt compromised a real PHP server. We also lack a reliable count of exposed installations still unpatched or relying entirely on partial mitigations. More exploitable variants may exist beyond the repaired root causes.
My bet: before 2027 ends, major managed PHP hosts will measure critical runtime mitigation in hours. Any security handbook still promising a seven-day patch window belongs beside that Obama-era plugin.
Frequently asked questions
Which PHP versions fix the PHP2Shell vulnerabilities?
PHP operators should update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, depending on the supported branch. Vendor-maintained distributions may provide verified backports with different version strings. After installation, restart Apache, PHP-FPM workers, containers or the entire workload, then verify that the patched interpreter is actually running.
How do CVE-2026-109618 and CVE-2026-109619 enable remote code execution?
CVE-2026-109618 can corrupt memory when an out-of-memory bailout leaves internal request data partly initialized, enabling code execution before application code under documented mod_php conditions. CVE-2026-109619 leaves request-owned state pointing to freed memory across requests, allowing later requests to consume stale memory through persistent workers.
What role did AI-assisted research play in discovering PHP2Shell?
The underlying out-of-memory issue was first noticed by a contracted PHP core developer in 2024 during work on Quarkslab’s audit finding. In 2026, Calif demonstrated unconditional remote code execution, while OpenAI independently reported the root cause and OpenAI and Wiz supplied additional vectors. AI also assisted report validation and grouping.
Sources
- Primary trending article
- How the PHP Security Team Handles Your Reports
- PHP 8 ChangeLog
- RCE via OOM corruption
- RCE via stale global state
- Patch the Planet: global response coordination as agents uncover critical vulnerabilities